Block it at the commit
Hooks stop .env files, keys and secrets before they are committed. CI templates catch whatever slips through.
00:00since you opened this page
Spillkit is a free, open-source kit for engineering teams. It blocks secrets at the commit, finds every one already in your Git history, tells you what to rotate first, tracks down copies that survive deletion and writes the report your leadership needs.
Tested configs, step-by-step runbooks and a single command, leak, that does the slow parts for you.
Hooks stop .env files, keys and secrets before they are committed. CI templates catch whatever slips through.
Scan every commit on every branch, including secrets someone already deleted. Values are always redacted.
leak scanA plan from the scan, most dangerous first, with where to revoke each secret. Cloud keys and GitLab and Azure DevOps tokens are rotated step by step, the new one piped straight into your vault.
leak plan and leak rotateTurn the evidence into a print-ready report with the facts leadership needs to decide, and none of the secrets.
leak reportForks, mirrors and web archives keep copies long after the original is gone. leak hunt checks them all at once and saves every answer as evidence.
When a service is down or rate-limited, it says not checked and exits with code 4. It never guesses "clean".
leak hunt result.Everything below was produced by the toolkit on demo repositories.
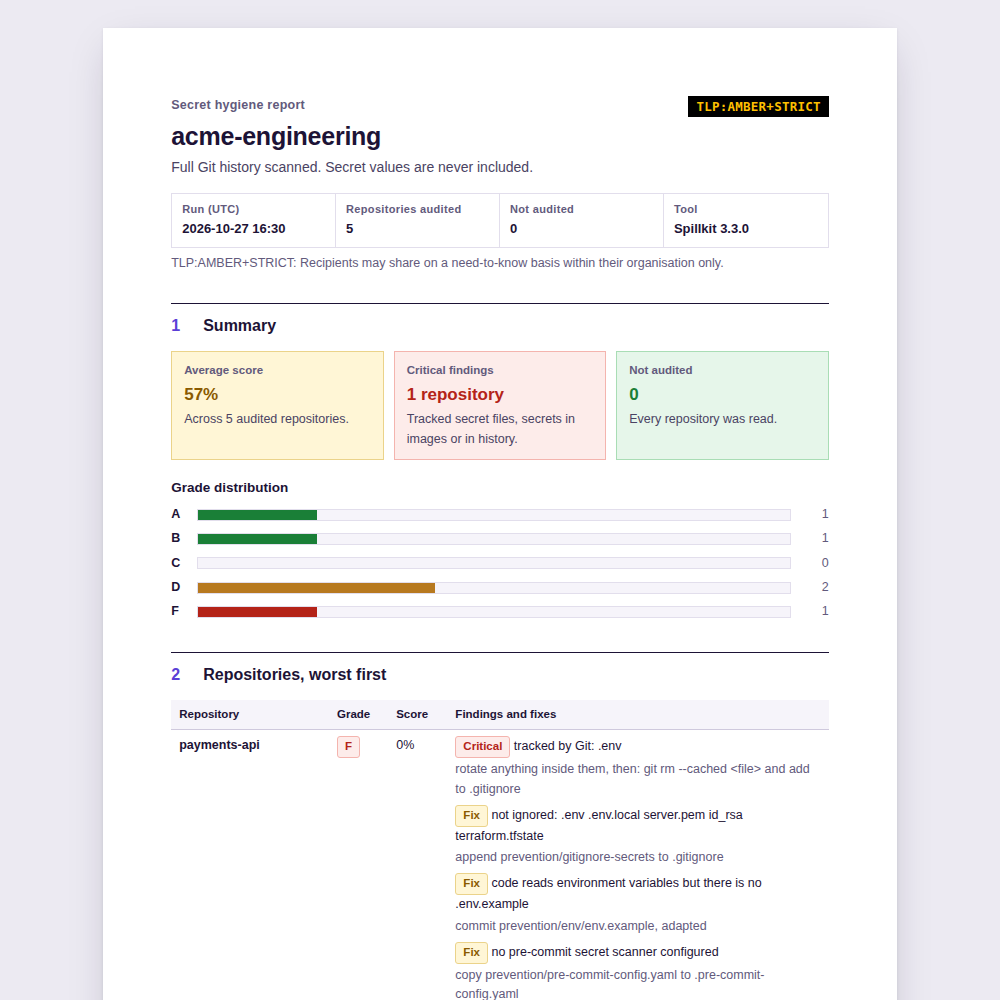
For platform and security teams
leak audit-org grades every repository from A to F and lists the exact fix for each gap, worst first.
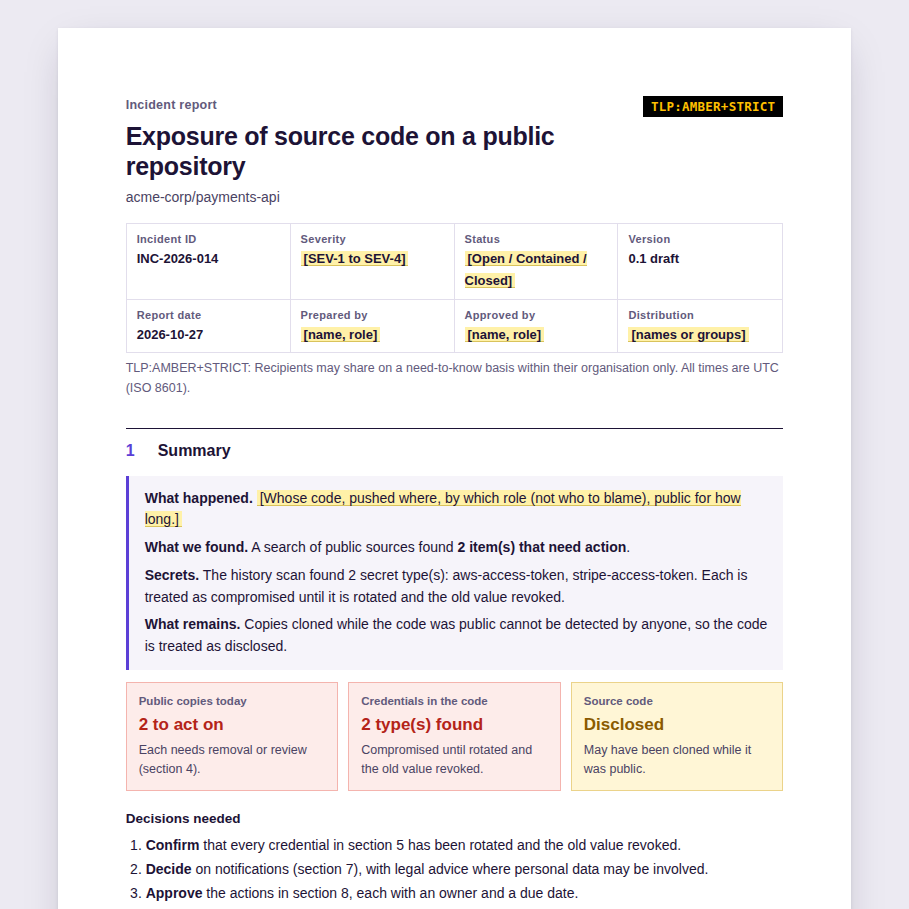
For leadership
leak report turns the hunt and the scan into a print-ready summary: what leaked, for how long, what was found and what happens next.
The first quarter of an hour decides how much a leak costs. The plan fits on one page, so nobody has to work out the order under pressure.
If a secret has leaked
Say it out loud. Tell your lead or security channel, then start the record: a UTC timeline, with the read-only steps below run in order.
leak respond owner/repoKeep the evidence. If the copy is yours and public by mistake, make it private. Don't delete it yet.
leak snapshot owner/repoRotate the most powerful secret first. Revoke the old value; adding a new one is not enough.
leak rotate aws-keyScan the whole history for every other secret, then put them in order.
leak scan ./repo && leak planRemove copies, check the logs, notify.
leak hunt owner/repoYou will run it during an incident, so every claim on this page can be verified.
Archives and images signed with Sigstore, with an SBOM and SLSA provenance. Verify one
A scanner error or an unreachable source is reported as not checked, never as clean.
No command prints or tests a secret. Tokens never appear in process lists or logs.
OpenSSF Scorecard, CodeQL and 60 tests on Linux and macOS for every change. See the score
One line on Linux and macOS, checked against the signed release, or Homebrew. Or run the signed container image, or add the toolkit to your pipeline and commit hooks.
Works with
# No root. Verifies the SHA-256, and the signature if cosign is installed.
curl -fsSL https://github.com/aboutBilal/spillkit/releases/latest/download/install.sh \
  | bash
leak demo   # see it work in a minute, on a leak made for the purpose
# macOS and Linux. Brings gitleaks, jq and, on macOS, a current bash.
brew install aboutbilal/tap/spillkit
leak demo # see it work in a minute, on a leak made for the purpose# No local dependencies. Signed image for amd64 and arm64.
docker run --rm -v "$PWD:/repo" ghcr.io/aboutbilal/spillkit audit /repo
docker run --rm -v "$PWD:/repo" ghcr.io/aboutbilal/spillkit scan /repo# Needs bash 4.4+, git, curl, jq, and gitleaks or Docker.
git clone https://github.com/aboutBilal/spillkit.git
cd spillkit && make install
leak doctor
leak audit .# .github/workflows/secrets.yml
on: [push, pull_request]
permissions:
contents: read
jobs:
secrets:
runs-on: ubuntu-latest
steps:
- uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1
with: { fetch-depth: 0, persist-credentials: false }
- uses: aboutBilal/spillkit@v3.8.1 # pin to a commit SHA in production
with:
mode: scan # scan, audit, audit-org or hunt# .pre-commit-config.yaml
repos:
- repo: https://github.com/aboutBilal/spillkit
rev: v3.8.1
hooks:
- id: forbid-secret-files # blocks .env, keys, state files
- id: leak-guard # also scans staged changes with gitleaksscan, audit and plan run entirely on your machine, and rotate uses your own cloud CLI, or the GitLab API, only for the steps you apply. hunt and audit-org send only repository names, account names and commit IDs to public services.audit-org grades whole organisations on all four.In a real leak, that's long enough for someone to find a key. Set the toolkit up before you need it.